Learning SQL Injection with OWASP Juice Shop: One Quote at a Time
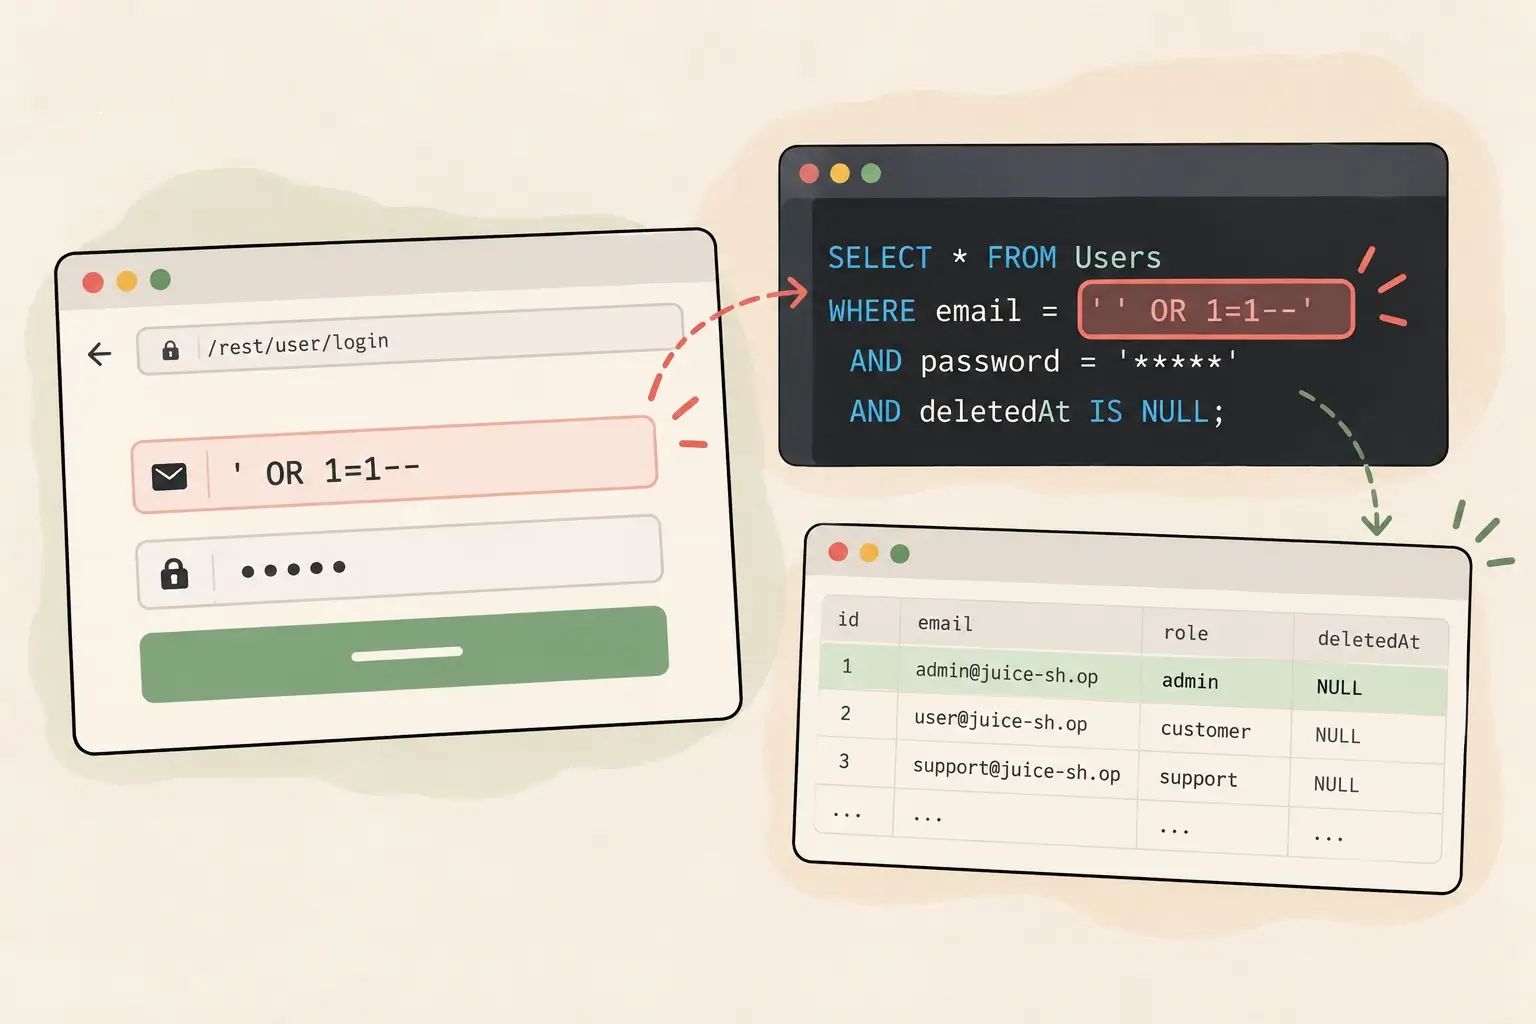
What happens when a single quotation mark changes the meaning of an SQL query? I explored SQL injection hands-on using OWASP Juice Shop, an intentionally vulnerable application, and discovered that understanding a security vulnerability takes more than memorising a payload. Sometimes, you have to stop, count the quotation marks, and work out exactly what’s happening.
Read article →